Showing posts with label cryptolocker. Show all posts

Saturday, 23 March 2019

Analysis of LockerGoga Ransomware


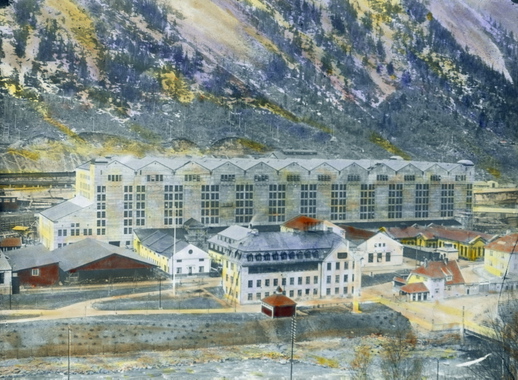
Картинки по запросу Norsk Hydro
Norsk Hydro back in 1905. 
Source: https://commons.wikimedia.org/wiki/File:Rjukan_fabrikker_-_Norsk_Hydro.jpg

This week BleepingComputer reported that LockerGoga ransomware was allegedly responsible for disrupting the Norsk Hydro's IT control system and forced the Norwegian industrial giant to switch to the manual operation mode. Later, according to Motherboard, this ransomware disrupted IT services of the two more US chemical companies Hexion and Momentive. Thus, it seems that the attackers behind LockerGoga target critical infrastructure and those mentioned above are not the only victims of the ransomware up to the moment. Further, we provide a detailed analysis of the ransomware encryption process.

Sunday, 4 February 2018

Thursday, 10 August 2017

Serpent Ransomware Analysis

The new Octopus cryptolocker being an offspring of the Serpent/Zyklon/WildFire/HadesLocker families shows that .NET ransomware can be not an easy meat for a reverse engineer. It leverages several types of obfuscation, code encryption, and anti-debugging to protect its C# code from decompilation and analysis.

Monday, 7 August 2017

Spora Ransomware Analysis


Similar to Cerber (Ferber) ransomware, Spora has its own intricate encryption file format and does not encrypt the whole file. The encryption block size varies depending on a file size.

Friday, 28 July 2017

New variant of Cerber ransomware (Ferber) analyzed


This summer Cerber is on duty. It comes via spear-phishing emails, bypasses antiviruses leveraging polymorphic encryption and API calls obfuscation. The cryptolocker can be easily customized for every target by embedding the JSON-formatted configuration data encrypted with RC4-128 (the decrypted config is on Github for cfd2d6f189b04d42618007fc9c540352). The file encryption scheme 'master RSA-2048 key'-> 'session RSA-880' -> 'file's RC4-128' used by Cerber is not breakable. Cerber scans the IP ranges specified by CIDRs in the config for the C&C server. 

Wednesday, 12 July 2017

Targeted attack with PowerShell ransomware comes undetected


The undetected PowerShell ransomware was used to attack the popular German car dealer. The attack launched through the spear phishing email looked like a mail delivery notification.

Wednesday, 28 June 2017

EternalPetya / NotPetya Ransomware Analysis


The new modification of Petya, which we named EternalPetya (because of using EternalBlue and EternalRomance exploits), caused surprisingly big infection outbreak in Ukraine and Russia.

Saturday, 3 June 2017

XData ransomware attacked users in Ukraine


On May 18, the author(s) of XData ransomware ran the massive attack against Ukrainian users supposedly leveraging the EternalBlue exploit as well as an ordinary spearphishing email delivery method. A week later, an anonymous user, supposedly the author of AES-NI ransomware the XData is based on, released the master private key. Currently, the XData decryption tools are available. We analysed the XData code and found two host-based 'kill-switches', one of them is about detecting an antivirus running on an infected machine.

Wednesday, 17 May 2017

Ransomware Protection Test - April 2017


During the last decade, ransomware (cryptolockers) show sustainable growth that can be explained by an effective business model that incorporates an anonymous payment system (Bitcoin) and network (TOR). This allows attackers to go untraceable and unpunished in their criminal activities.

In this regard, antiviruses and backup solutions come to protect you against ransomware and eliminate infection consequences. However, based on our incidents investigation experience, most of the ransomware infections in organizations happened with an antivirus installed and turned on. This can be explained by the fact, that the new ransomware variants employ polymorphic encryption with code obfuscation [1], broken PE headers [2], and scripting languages [3, 4]. All these help attackers bypass antivirus signature-based protection giving a chance for behavior blockers and anti-ransomware solutions to come into play. Therefore, it is essential to test security solutions by simulating the real-world ransomware attacks.

First, we tried the RanSim ransomware simulation software made by KnowBe4 [5] to verify if an antivirus can block a ransomware attack. However, RanSim has several limitations. The most principal one is that antiviruses block the RanSim executables underway using simple blacklists before the actual test scenarios are run. The question then arises as to how to bypass antivirus signature protection to run ransomware test scenarios that will test the antivirus behavior blocker or anti-ransomware protection only.

To solve the problem of testing anti-ransomware solutions, we looked into the successful real-world ransomware attacks to find out the techniques that help malware to go unnoticed. As a result, we created the ransomware testing framework called NioCryptoSim [6] written mostly in Python. The test suite includes three false positive tests and 15 tests simulating the base cryptolocker functions as well as complete models imitating the behavior of some real-world ransomware.

As a result, we tested 22 top antiviruses and one backup solution with the anti-ransomware solution from Acronis using the NioCryptoSim testing framework.

See the full report by the link.

Monday, 15 May 2017

WannaCry 2.0: Indicators of Compromise


WannaCry (WannaCryptor) is becoming probably the most popular cryptolocker in the history of ransomware. It has nothing new in terms of files encryption (RSA + AES using MS CryptoAPI) but uses MS17-010 (a.k.a. ETERNALBLUE named by NSA) vulnerability to propagate itself through local networks using the Server Message Block (SMB) protocol as a network worm resulting in thousands of infections of Windows machines that have not been updated so far.

Monday, 3 April 2017

Beware of Cerber in your parcel


New Cerber ransomware comes through parcel delivery notifications with zip attachments.

Friday, 17 March 2017

Shade ransomware comes through billing notifications


We are seeing the numerous infections by the new version of the Shade cryptolocker during the last week in Ukraine. The Shade has been leveraging a cheap and effective email delivery channel. The attack is run with the help of fake emails sent on behalf of Ukrainian financial institutions (e.g. PrivatBank, the Ukrainian Tax Office) from the hacked email accounts, most of them belong to organizations in the gov.ua TLD. The subject of these emails is bills or indebtedness that a victim needs to pay.

Thursday, 2 February 2017

Decrypting DeriaLock


Recently, our laboratory analyzed the new version of DeriaLock (MD5: 0a7b70efba0aa93d4bc0857b87ac2fcb).

This version of DeriaLock is unique because of two reasons. First, it demands to pay the 30 USD/EUR ransom to the Skype account. Second, DeriaLock incorporates three types of functionality: SystemLocker, CryptoLocker, and FileKiller within a single attack.

If you managed to remove the DeriaLock infection and keep your encrypted files, you can start now decrypting your documents using the encryption key and initialization vector calculated by our script based on the password string extracted from the analyzed version of DeriaLock:

AES-256 key: 9c9e1ba2ee5b86494b7e1ebba6420ee6ab64ce6d678604eb5b5049b210693743
IV: 9fa4ed4d89b04ee7f3b74c9b46588e18

To decrypt '.deria' files, you can use OpenSSL tool specifying the discovered key and initialization vector. For example:
openssl aes-256-cbc -d -in photo.png.deria -K 9c9e1ba2ee5b86494b7e1ebba6420ee6ab64ce6d678604eb5b5049b210693743 -iv 9fa4ed4d89b04ee7f3b74c9b46588e18 -out photo.png
Or use our Python script or executable to decrypt all '.deria' files that can be found on your computer.

Sunday, 20 December 2015

VaultCrypt: From Russia with Love

During the last several months Ukrainian Cyberpolice recorded many incidents all over the country with VaultCrypt. We decided to shed light on the issue. VaultCrypt is a cryptolocker having the similar to TeslaCrypt scheme using Tor and Bitcoins to pay a ransom, but simpler in implementation.